When I decided to pursue the Security Operations Center (SOC) path in cybersecurity, I knew I wanted to understand the concepts, not just memorize them for an exam.
I’m currently preparing for the CompTIA Security+ certification, and I’ve been learning with Professor Messer’s YouTube lessons. Every study session has introduced me to concepts that make me appreciate how organizations protect their systems and data.
I also explored offensive security a little in the past, and that experience actually gave me the motivation to focus on the Blue Team side of cybersecurity.
Here are some of the concepts I’ve learned so far.
Understanding Security Controls
One of the first things I learned was that security isn’t just about installing antivirus software.
There are different categories of security controls.
Technical Controls
These are technology-based controls implemented through systems and software.
Examples include:
-
Firewalls
-
Antivirus software
-
Operating system security features
-
Access control systems
Managerial (Administrative) Controls
These focus on planning, governance, and security policies.
Examples include:
-
Security policies
-
Risk management
-
Security procedures
Operational Controls
These are controls carried out primarily by people.
Examples include:
-
Security awareness training
-
Security guards
-
Incident response procedures
Physical Controls
These protect physical assets.
Examples include:
-
Locks
-
Fences
-
Badge readers
-
Guard shacks
Types of Security Controls
I also learned that controls can serve different purposes.
|
Control Type |
Purpose |
|---|---|
|
Preventive |
Stops attacks before they happen. |
|
Deterrent |
Discourages attackers from trying. |
|
Detective |
Identifies suspicious activity. |
|
Corrective |
Helps recover after an incident. |
|
Compensating |
Provides alternative protection when another control isn’t enough. |
|
Directive |
Guides users through policies and procedures. |
The CIA Triad
This is probably one of the most important foundations in cybersecurity.
Confidentiality
Only authorized users should access sensitive information.
Examples:
-
Encryption
-
Access controls
-
Multi-factor authentication
Integrity
Data should not be modified without detection.
Examples:
-
Hashing
-
Digital signatures
Availability
Systems should remain accessible when users need them.
Examples:
-
Redundancy
-
Fault tolerance
-
Regular patching
What Non-Repudiation Really Means
I found this concept interesting because it’s about accountability.
Non-repudiation means someone cannot reasonably deny performing an action.
For example, if a document is digitally signed, that signature can help prove who approved it.
I also learned about:
-
Proof of integrity through hashing.
-
Proof of origin through digital signatures and cryptography.
The AAA Framework
Another important topic was the AAA Framework.
Authentication
Prove you are who you claim to be.
Authorization
Determine what you’re allowed to access after authentication.
Accounting
Track activities such as:
-
Login time
-
Logout time
-
Resources used
-
Data transferred
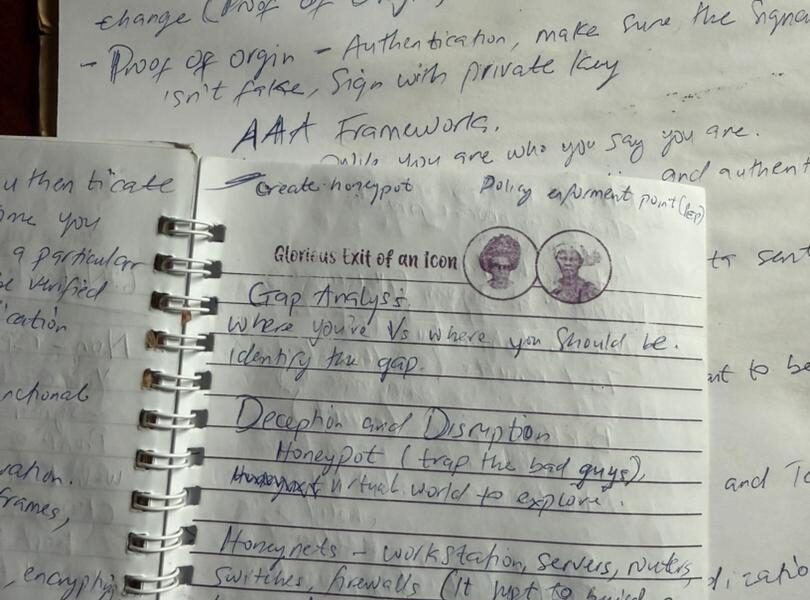
Gap Analysis Became One of My Favorite Topics
This is honestly one of the concepts that stood out to me.
Gap analysis asks a simple question.
Where are we now, where do we want to be, and what do we need to do to bridge that gap?
Organizations can use frameworks like:
-
NIST
-
ISO
-
IEC
Or they can create their own internal baseline.
That way, they always have a measurable standard they’re working toward.
Learning About Zero Trust
Zero Trust follows one simple principle.
Never trust. Always verify.
Instead of assuming someone is trustworthy after logging in once, every access request should be verified based on identity, device, and context.
Multi-factor authentication is one practical example of this approach.
Data Plane vs Control Plane
I also started learning how network devices operate behind the scenes.
Data Plane
Handles traffic processing by:
-
Forwarding packets
-
Encrypting data
-
Performing NAT
-
Processing network traffic
Control Plane
Makes decisions about how traffic should be handled through policies and routing decisions.
Deception and Disruption
This was another interesting topic because it turns defense into something proactive.
I learned about:
-
Honeypots
-
Honeynets
-
Honeyfiles
-
Honeytokens
A honeypot, for example, can attract attackers into a monitored environment so defenders can study their behavior without exposing real assets.
My Biggest Takeaway So Far
I’m still early in this journey, but every concept makes cybersecurity feel more practical.
The goal isn’t just to pass CompTIA Security+.
The goal is to build the knowledge and mindset needed to become a capable SOC Analyst.
One concept at a time.
One step closer to the Blue Team.
Frequently Asked Questions
Is CompTIA Security+ good for aspiring SOC Analysts?
Yes. Security+ provides foundational knowledge in networking, security controls, risk management, cryptography, and incident response, making it one of the most recognized entry-level cybersecurity certifications.
What is the CIA Triad?
The CIA Triad stands for Confidentiality, Integrity, and Availability. It forms the foundation of information security.
What is Zero Trust?
Zero Trust is a security model that requires continuous verification before granting access to resources instead of automatically trusting users or devices.
Why is Gap Analysis important?
Gap analysis helps organizations compare their current security posture with their desired security baseline and identify what improvements are needed.